Things we made and we loved it
Agent Security is the gateway itself, open sourced. The other two were built beside it, then given away. All three run on your own machine, need no account, and cost nothing.
Three are here today, with more to come. What each one does, and how to run it, below.
Agent Security
This one is the gateway itself: the same product SolonGate sells, open sourced and free to run against your own agents, no account and no network call.
Every tool call passes five layers before it runs: tamper protection, a rate limit, policy rules compiled from JSON, secret detection, and an egress check on what an upload would actually send. Any layer can refuse the call, and the refusal is logged before the agent hears no.
Pattern matching can't catch a script the agent writes and then runs, so solongate protect locks the path at the OS level: chflags on macOS, chattr +i on Linux, an ACL deny on Windows. It's in place before the agent's first instruction, and nothing it runs can remove it.
$ git clone https://github.com/solongate/agent-security.git
cd agent-security
./scripts/shell/install.sh
PSIRTMap
A package scanner tells you openssl 3.0.8 matches a vulnerability. PSIRTMap answers the next question: which shipped product versions actually contain it.
It works on a product release, not an image or a filesystem. Import a release's CycloneDX SBOM and it derives OSV identities from the package URLs, then tracks findings across scans as new, existing, reopened, or no longer matched.
A version match is evidence, not a verdict; the final call is a human assessment, appended with a reviewer, reason and timestamp, never overwritten. Everything is local: one SQLite file, no server, no account. Only updating the vulnerability snapshot touches the network.
$ curl -fsSL https://raw.githubusercontent.com/solongate/psirtmap/main/scripts/install.sh | sh
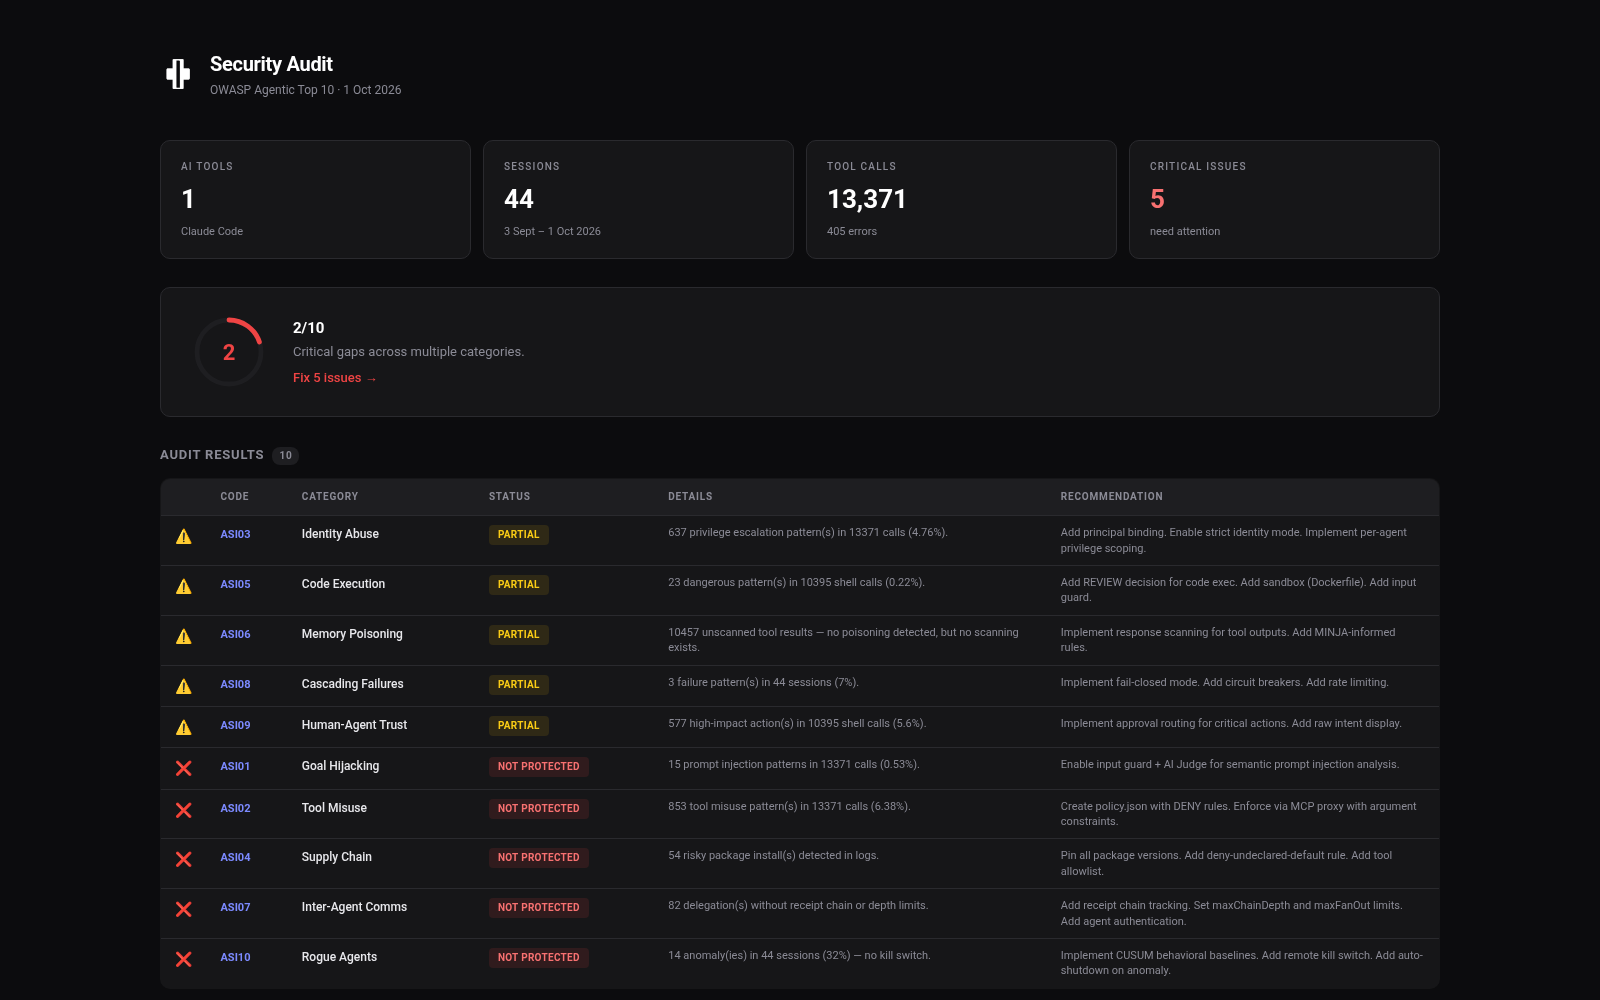
solongate-audit
Your coding agents have been running tools for months, and the record is already on your disk. solongate-audit reads those session logs and checks the patterns against the OWASP Agentic Top 10 for 2026.
It reads what's already there, no instrumentation. Claude Code, Gemini CLI and OpenClaw logs are found at their default locations, with extra directories if needed. Nothing leaves the machine.
Each of the ten categories comes back PROTECTED, PARTIAL or NOT PROTECTED with a count behind it. The score is out of ten; exit code is zero at seven or better, so it can gate a build. Reports export to JSON, CSV, HTML or PDF.
Install from a checkout for now: clone, npm install, npm run build, run dist/index.js. The published npm package was taken down in June, so the README's npx line won't resolve.
$ git clone https://github.com/solongate/solongate-audit